Look
You send the URL and hosting access. We scan before touching anything and tell you what we found, what it costs and how long it takes.
We clean infected WordPress sites, remove the backdoors that let it happen, and harden what is left so it does not come back. Fixed prices, and a clear answer on how it got in.
Almost nothing that hits a WordPress site is personal. Bots scan the whole internet for one outdated plugin, one weak password, one file left behind by a developer who moved on. When they find it, they take what they can and leave a way back in.
That is why cleaning the visible damage is not enough. If the backdoor stays, the malware returns within days and you pay someone to remove it again. We work the other way round: find the entry point first, close it, then clean what it did.
The visible damage is removed. The way in stays open. It comes back within the week.
The entry point is closed first, then the payload is removed, then the site is hardened so the same route does not work twice.
Every job covers the fundamentals. What changes is how much of the site we rebuild around them.
Full scan of files and database
Both are checked. Database injections and disguised files are more common than a visibly broken theme.
Malware, injected code and backdoors removed
The payload and the way in, together. Removing one without the other is why sites get reinfected.
Core files verified against the originals
Every WordPress core file is compared against the original and replaced where it was modified.
Passwords and security keys rotated
Admin accounts, database user and WordPress salts. Any session an attacker still had is invalidated.
A backup of the infected state, kept
Taken before anything is touched, so nothing is lost and the infection can be examined rather than guessed at.
Hardening and firewall rules
Login locked down, file permissions corrected, and firewall rules applied so the same route does not work twice.
A written report on how it got in
What was found, what was removed, and the entry point. Included in every job, not sold separately.
Scanned
Files + database
Turnaround
Same or next day
Guarantee
30 days
Firewall
Per site, tuned to the stack
Nulled plugins
Replaced, not restored
Almost every infection we clean came through one of these. None of them are exotic.
Plugins
Outdated or abandoned
A plugin that has not been updated in two years is not a feature, it is an open door. Cracked plugins are worse: the crack is often the payload itself.
Access
Weak and reused passwords
Admin accounts with passwords that appear in every leak list, and nothing limiting how many times a bot can guess.
Hosting
Shared accounts and old PHP
One infected site on the same account can reach the others. Old PHP versions carry holes nobody patches any more.
Leftovers
Files nobody remembers
Test installs, old backups and forgotten upload folders sitting in the web root, still executable.
Most sites are back to normal the same day. Bigger jobs take longer, and you will know which one yours is before we start.
You send the URL and hosting access. We scan before touching anything and tell you what we found, what it costs and how long it takes.
A full backup of the infected state is taken first, so nothing is lost and the infection can be studied rather than guessed at.
Malware, injected code and backdoors removed. Core files replaced from the originals. Passwords and security keys rotated.
Login locked down, file permissions corrected, firewall rules applied, and anything cracked replaced or licensed properly.
Blacklists, browser warnings and host suspensions resolved, and you get the written report.
Spam URLs the infection published are removed from Google, the sitemap is rebuilt from the real pages, and Search Console is checked for manual actions and security issues. A site can come back clean and still rank for somebody else’s spam if this step is skipped.
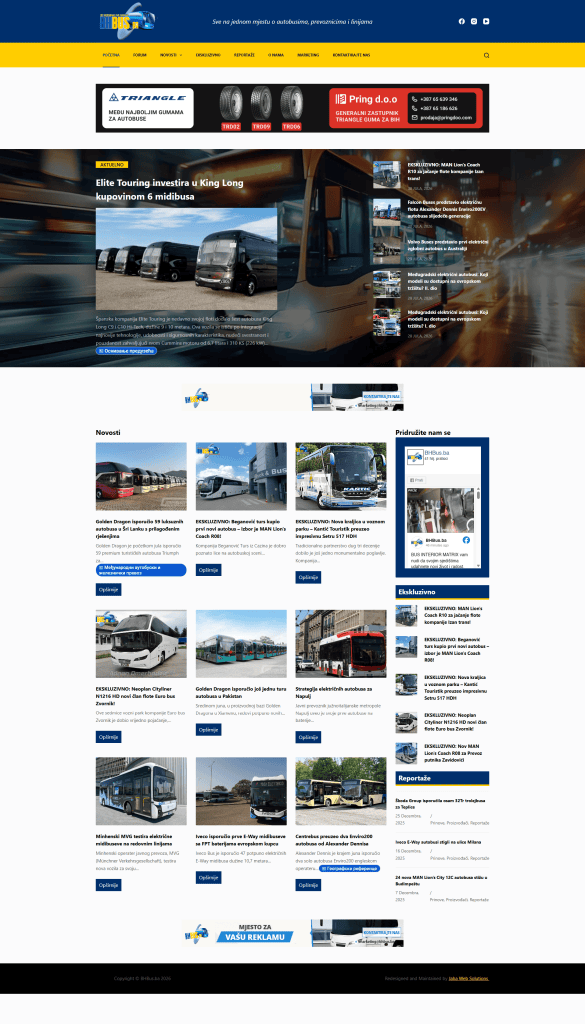
A hacked portal rebuilt on a dedicated server, with the forum moved and rankings kept.
Read the case studyMost cleanups hand back a working site and no explanation. Without the entry point, you are paying for the same job again next month.
You know the cost before we start. A cleanup that turns out worse than it looked is our problem, not a bigger invoice.
If the site runs nulled plugins they get replaced or licensed properly. Restoring them restores the infection.
Three ways to deal with an infected site, depending on how deep it went.
Malware removal
Your site cleaned in place. Same theme, same plugins, same setup.
Clean reinstall
Most popularA fresh install with your theme and plugins put back clean, for sites that were hit hard.
Rebuild
For sites where there is nothing safe left to keep.
Every cleanup is covered for 30 days: if the same infection returns and nothing new was installed, we clean it again at no cost. Malware cleanup is included in every care plan, and sites we maintain are covered for as long as we maintain them.
Not included
Same day in most cases. Send the URL and hosting access and you get a scan result and a fixed price before any work begins.
That is the most common WordPress infection there is. The attacker publishes thousands of hidden pages on your domain and lets Google index them, so your site starts ranking for casinos, pills or Japanese text you never wrote. Cleaning the files is only half of it. Pages that were already indexed have to be pulled out of search too, or your results stay poisoned long after the site itself is clean.
Through Search Console: the injected URLs are removed from the index, the sitemap is rebuilt from the real pages, and manual actions and security issues are cleared. It is slow work and most cleanups skip it, which is why a site can come back clean and still rank for somebody else’s spam.
No. A full backup of the infected state is taken before anything is touched, and content is carried over rather than recreated. The only things that do not come back are cracked plugins and files that were pure malware.
You get a written report listing what was found, what was removed and how it got in. The site is rescanned after the work, and the entry point is closed rather than left for next time.
If the same infection returns within 30 days and nothing new was installed in the meantime, we clean it again at no cost. Sites on one of our care plans are covered for as long as we maintain them.
Yes. Suspensions and blacklist entries are part of the job. We clean the site, then submit the review requests to the host, to Google and to the browser vendors.
You need updates, backups and someone watching more than you need another plugin. Hardening and firewall rules are included in every cleanup. Keeping them that way over time is what a care plan does.
That is included in every cleanup, not sold separately. If you only want an assessment, ask for a free audit and we will tell you what we can see from the outside.